|
|
|
|||||||
| Register | iSpy | Downloads | New Posts | Donate | Unanswered Posts | Member List | Search |
|
Computer Juice raffle
- Win PC hardware of your choice worth £500 / 680 / $1000 -
Enter HERE!
|
|
|
Computer Juice - Forums - HJT log help |

|
|
|
Thread Tools |
|
#
1
 27-04-2008, 01:59 AM |
||||
|
||||

HJT log help
I don't know what to look for. Anyone see something that shouldn't be there.
Logfile of Trend Micro HijackThis v2.0.2 Scan saved at 9:55:40 PM, on 4/26/2008 Platform: Windows XP SP2 (WinNT 5.01.2600) MSIE: Internet Explorer v7.00 (7.00.6000.16640) Boot mode: Normal Running processes: C:\WINDOWS\System32\smss.exe C:\WINDOWS\system32\winlogon.exe C:\WINDOWS\system32\services.exe C:\WINDOWS\system32\lsass.exe C:\WINDOWS\system32\Ati2evxx.exe C:\WINDOWS\system32\svchost.exe C:\WINDOWS\System32\svchost.exe C:\WINDOWS\system32\Ati2evxx.exe C:\WINDOWS\system32\spoolsv.exe C:\WINDOWS\Explorer.EXE C:\Program Files\Microsoft IntelliType Pro\type32.exe C:\Program Files\Microsoft IntelliPoint\point32.exe C:\WINDOWS\SOUNDMAN.EXE C:\Program Files\ATI Technologies\ATI.ACE\Core-Static\MOM.EXE C:\Program Files\Java\jre1.6.0_05\bin\jusched.exe C:\Program Files\Adobe\Acrobat 8.0\Acrobat\Acrotray.exe C:\Program Files\iTunes\iTunesHelper.exe C:\Program Files\Common Files\Ahead\Lib\NMBgMonitor.exe C:\WINDOWS\system32\ctfmon.exe C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe C:\WINDOWS\system32\svchost.exe C:\Program Files\Viewpoint\Common\ViewpointService.exe C:\Program Files\Common Files\Ahead\Lib\NMIndexingService.exe C:\Program Files\Common Files\Ahead\Lib\NMIndexStoreSvr.exe C:\Program Files\iPod\bin\iPodService.exe C:\Program Files\Common Files\Macrovision Shared\FLEXnet Publisher\FNPLicensingService.exe C:\Program Files\ATI Technologies\ATI.ACE\Core-Static\ccc.exe J:\Apps\HiJackThis.exe C:\Program Files\Mozilla Firefox\firefox.exe C:\Program Files\AIM6\aim6.exe C:\Program Files\AIM6\aolsoftware.exe R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = < Link hidden. Register for free to see this link! > R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = < Link hidden. Register for free to see this link! > R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = < Link hidden. Register for free to see this link! > R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = < Link hidden. Register for free to see this link! > R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Int ernet Settings,ProxyOverride = *.local O2 - BHO: Adobe PDF Reader Link Helper - {06849E9F-C8D7-4D59-B87D-784B7D6BE0B3} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelper.dll O2 - BHO: SSVHelper Class - {761497BB-D6F0-462C-B6EB-D4DAF1D92D43} - C:\Program Files\Java\jre1.6.0_05\bin\ssv.dll O2 - BHO: Adobe PDF Conversion Toolbar Helper - {AE7CD045-E861-484f-8273-0445EE161910} - C:\Program Files\Adobe\Acrobat 8.0\Acrobat\AcroIEFavClient.dll O3 - Toolbar: Adobe PDF - {47833539-D0C5-4125-9FA8-0819E2EAAC93} - C:\Program Files\Adobe\Acrobat 8.0\Acrobat\AcroIEFavClient.dll O4 - HKLM\..\Run: [type32] "C:\Program Files\Microsoft IntelliType Pro\type32.exe" O4 - HKLM\..\Run: [IntelliPoint] "C:\Program Files\Microsoft IntelliPoint\point32.exe" O4 - HKLM\..\Run: [SoundMan] SOUNDMAN.EXE O4 - HKLM\..\Run: [StartCCC] "C:\Program Files\ATI Technologies\ATI.ACE\Core-Static\CLIStart.exe" O4 - HKLM\..\Run: [EPSON Stylus CX3800 Series] C:\WINDOWS\System32\spool\DRIVERS\W32X86\3\E_FATIA CA.EXE /P26 "EPSON Stylus CX3800 Series" /O6 "USB001" /M "Stylus CX3800" O4 - HKLM\..\Run: [NeroFilterCheck] C:\Program Files\Common Files\Ahead\Lib\NeroCheck.exe O4 - HKLM\..\Run: [SunJavaUpdateSched] "C:\Program Files\Java\jre1.6.0_05\bin\jusched.exe" O4 - HKLM\..\Run: [Acrobat Assistant 8.0] "C:\Program Files\Adobe\Acrobat 8.0\Acrobat\Acrotray.exe" O4 - HKLM\..\Run: [Adobe Reader Speed Launcher] "C:\Program Files\Adobe\Reader 8.0\Reader\Reader_sl.exe" O4 - HKLM\..\Run: [QuickTime Task] "C:\Program Files\QuickTime\qttask.exe" -atboottime O4 - HKLM\..\Run: [iTunesHelper] "C:\Program Files\iTunes\iTunesHelper.exe" O4 - HKCU\..\Run: [BgMonitor_{79662E04-7C6C-4d9f-84C7-88D8A56B10AA}] "C:\Program Files\Common Files\Ahead\Lib\NMBgMonitor.exe" O4 - HKCU\..\Run: [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe O4 - Startup: Epson all-in-one Registration.lnk = D:\Titles\Ereg\EPSONREG.EXE O8 - Extra context menu item: Append to existing PDF - res://C:\Program Files\Adobe\Acrobat 8.0\Acrobat\ < Link hidden. Register for free to see this link! > O8 - Extra context menu item: Convert link target to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 8.0\Acrobat\ < Link hidden. Register for free to see this link! > O8 - Extra context menu item: Convert link target to existing PDF - res://C:\Program Files\Adobe\Acrobat 8.0\Acrobat\ < Link hidden. Register for free to see this link! > O8 - Extra context menu item: Convert selected links to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 8.0\Acrobat\ < Link hidden. Register for free to see this link! > O8 - Extra context menu item: Convert selected links to existing PDF - res://C:\Program Files\Adobe\Acrobat 8.0\Acrobat\ < Link hidden. Register for free to see this link! > O8 - Extra context menu item: Convert selection to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 8.0\Acrobat\ < Link hidden. Register for free to see this link! > O8 - Extra context menu item: Convert selection to existing PDF - res://C:\Program Files\Adobe\Acrobat 8.0\Acrobat\ < Link hidden. Register for free to see this link! > O8 - Extra context menu item: Convert to Adobe PDF - res://C:\Program Files\Adobe\Acrobat 8.0\Acrobat\ < Link hidden. Register for free to see this link! > O8 - Extra context menu item: E&xport to Microsoft Excel - res://C:\PROGRA~1\MICROS~4\OFFICE11\ < Link hidden. Register for free to see this link! > O9 - Extra button: (no name) - {08B0E5C0-4FCB-11CF-AAA5-00401C608501} - C:\Program Files\Java\jre1.6.0_05\bin\ssv.dll O9 - Extra 'Tools' menuitem: Sun Java Console - {08B0E5C0-4FCB-11CF-AAA5-00401C608501} - C:\Program Files\Java\jre1.6.0_05\bin\ssv.dll O9 - Extra button: Research - {92780B25-18CC-41C8-B9BE-3C9C571A8263} - C:\PROGRA~1\MICROS~4\OFFICE11\REFIEBAR.DLL O9 - Extra button: (no name) - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe O9 - Extra 'Tools' menuitem: @xpsp3res.dll,-20001 - {e2e2dd38-d088-4134-82b7-f2ba38496583} - C:\WINDOWS\Network Diagnostic\xpnetdiag.exe O9 - Extra button: Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe O9 - Extra 'Tools' menuitem: Windows Messenger - {FB5F1910-F110-11d2-BB9E-00C04F795683} - C:\Program Files\Messenger\msmsgs.exe O18 - Protocol: skype4com - {FFC8B962-9B40-4DFF-9458-1830C7DD7F5D} - C:\PROGRA~1\COMMON~1\Skype\SKYPE4~1.DLL O23 - Service: Apple Mobile Device - Apple, Inc. - C:\Program Files\Common Files\Apple\Mobile Device Support\bin\AppleMobileDeviceService.exe O23 - Service: Ati HotKey Poller - ATI Technologies Inc. - C:\WINDOWS\system32\Ati2evxx.exe O23 - Service: ATI Smart - Unknown owner - C:\WINDOWS\system32\ati2sgag.exe O23 - Service: FLEXnet Licensing Service - Macrovision Europe Ltd. - C:\Program Files\Common Files\Macrovision Shared\FLEXnet Publisher\FNPLicensingService.exe O23 - Service: iPod Service - Apple Inc. - C:\Program Files\iPod\bin\iPodService.exe O23 - Service: NBService - Nero AG - C:\Program Files\Nero\Nero 7\Nero BackItUp\NBService.exe O23 - Service: NMIndexingService - Nero AG - C:\Program Files\Common Files\Ahead\Lib\NMIndexingService.exe O23 - Service: Viewpoint Manager Service - Viewpoint Corporation - C:\Program Files\Viewpoint\Common\ViewpointService.exe -- End of file - 7270 bytes 
|
|
|
|
#
2
27-04-2008, 02:14 AM
|
||||
|
||||
HJT log help
Whats up Sideways.
You have Viewpoint installed. Viewpoint Media Player/Manager/Toolbar is considered as foistware instead of malware since it is installed without users approval but doesn't spy or do anything "bad". See < Link hidden. Register for free to see this link! > It is suggested to remove the program now. Go to Start > Settings > Control Panel > Add/Remove Programs and remove the following programs if present.
Once you have downloaded ViewpointKiller, unzip it to a convenient location such as your desktop. Run ViewpointKiller, and select File > Do All Killings Follow the prompts, selecting Yes or No , depending on which selection you are most comfortable with. A logfile will be created in the folder you unzipped ViewpointKiller to, please paste the contents here. ---------- I can see no indication of any antivirus software. Install antiVirus Software It is very important that you have antivirus software running on your computer. This alone can save you a lot of trouble with malware now and in the future. Install only one free AV. I recommend Avast! Home Free < Link hidden. Register for free to see this link! > < Link hidden. Register for free to see this link! > Once installed update the antivirus software It is imperative that you update your antivirus software at least once a week. The best solution is to enable automatic updates. ---------- Download Malwarebytes' Anti-Malware (MBAM) to your desktop from either of these two links.
Next post please add MBAM log Let me know what all is wrong now (if anything)
__________________
. 
Never argue with an idiot. They'll bring you down to their level, then beat you with experience.
.
. Last edited by evilfantasy : 27-04-2008 at 02:15 AM .
|
|
#
3
27-04-2008, 07:37 AM
|
||||
|
||||
HJT log help
Thanks for the help. I'm not experiencing any "problems" just rather be safe than sorry.
Malwarebytes' Anti-Malware 1.11 Database version: 689 Scan type: Full Scan (C:\|I:\|J:\|) Objects scanned: 87613 Time elapsed: 22 minute(s), 8 second(s) Memory Processes Infected: 0 Memory Modules Infected: 0 Registry Keys Infected: 1 Registry Values Infected: 0 Registry Data Items Infected: 0 Folders Infected: 0 Files Infected: 1 Memory Processes Infected: (No malicious items detected) Memory Modules Infected: (No malicious items detected) Registry Keys Infected: HKEY_CLASSES_ROOT\WUSN.1 (Adware.WhenUSave) -> Quarantined and deleted successfully. Registry Values Infected: (No malicious items detected) Registry Data Items Infected: (No malicious items detected) Folders Infected: (No malicious items detected) Files Infected: C:\WINDOWS\system32\GWLDO132.DLL (Trojan.Vundo) -> Quarantined and deleted successfully.
|
|
#
4
27-04-2008, 08:37 AM
|
||||
|
||||
HJT log help
Looks OK except for this
C:\WINDOWS\system32\GWLDO132.DLL
, I would like to make sure that no more Vundo files are left over.
Please download Combofix by sUBs from one of the below links. (Try all three if necessary)
Next post: Combofix log
__________________
.
Never argue with an idiot. They'll bring you down to their level, then beat you with experience.
.
.
|
|
#
5
27-04-2008, 07:18 PM
|
||||
|
||||
HJT log helpMicrosoft Windows XP Professional 5.1.2600.2.1252.1.1033.18.1391 [GMT -4:00] Running from: I:\Downloads\ComboFix.exe * Created a new restore point WARNING -THIS MACHINE DOES NOT HAVE THE RECOVERY CONSOLE INSTALLED !! . ((((((((((((((((((((((((((((((((((((((( Other Deletions ))))))))))))))))))))))))))))))))))))))))))))))))) . C:\Documents and Settings\Jeffrey\Application Data\inst.exe C:\WINDOWS\system32\dllcache\spoolsv.exe . ((((((((((((((((((((((((( Files Created from 2008-03-27 to 2008-04-27 ))))))))))))))))))))))))))))))) . . (((((((((((((((((((((((((((((((((((((((( Find3M Report )))))))))))))))))))))))))))))))))))))))))))))))))) )) . . ((((((((((((((((((((((((((((((((((((( Reg Loading Points )))))))))))))))))))))))))))))))))))))))))))))))))) . . *Note* empty entries & legit default entries are not shown REGEDIT4 [HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\Curre ntVersion\Run] "Aim6"="" [] [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\Curr entVersion\Run] [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\drivers32] "vidc.ffds"= C:\PROGRA~1\COMBIN~1\Filters\FFDShow\ff_vfw.dll [HKEY_LOCAL_MACHINE\software\microsoft\security center] "AntiVirusOverride"=dword:00000001 [HKLM\~\services\sharedaccess\parameters\firewallpo licy\standardprofile\AuthorizedApplications\List] "%windir%\\system32\\sessmgr.exe"= "C:\\Program Files\\Common Files\\AOL\\Loader\\aolload.exe"= "C:\\Program Files\\AIM6\\aim6.exe"= "C:\\Novell\\GroupWise\\grpwise.exe"= "C:\\Novell\\GroupWise\\notify.exe"= "C:\\Program Files\\World of Warcraft\\BackgroundDownloader.exe"= "C:\\Program Files\\Skype\\Phone\\Skype.exe"= "%windir%\\Network Diagnostic\\xpnetdiag.exe"= "C:\\Program Files\\iTunes\\iTunes.exe"= [HKLM\~\services\sharedaccess\parameters\firewallpo licy\standardprofile\GloballyOpenPorts\List] "3724:TCP"= 3724:TCP:Blizzard Downloader: 3724 [HKEY_CURRENT_USER\software\microsoft\windows\curre ntversion\explorer\mountpoints2\E] \Shell\AutoRun\command - E:\Launcher.exe [HKEY_CURRENT_USER\software\microsoft\windows\curre ntversion\explorer\mountpoints2\F] \Shell\AutoRun\command - F:\launcher.exe [HKEY_CURRENT_USER\software\microsoft\windows\curre ntversion\explorer\mountpoints2\{8c762673-747b-11dc-b053-00121755d2c1}] \Shell\AutoRun\command - F:\LaunchU3.exe -a *Newly Created Service* - AAVMKER4 *Newly Created Service* - ASWFSBLK *Newly Created Service* - ASWMON2 *Newly Created Service* - ASWRDR *Newly Created Service* - ASWSP *Newly Created Service* - ASWTDI *Newly Created Service* - ASWUPDSV *Newly Created Service* - AVAST!_ANTIVIRUS *Newly Created Service* - AVAST!_MAIL_SCANNER *Newly Created Service* - AVAST!_WEB_SCANNER *Newly Created Service* - CATCHME . Contents of the 'Scheduled Tasks' folder - C:\Program Files\Apple Software Update\SoftwareUpdate.exe - C:\PROGRA~1\SMARTD~1\Messages\SDNotify.exeW-PTE -V810 -SSDU.ini -A -M < Link hidden. Register for free to see this link! > -D0 -T -N -X . ************************************************** ************************ catchme 0.3.1353 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, < Link hidden. Register for free to see this link! > Windows 5.1.2600 Service Pack 2 NTFS scanning hidden processes ... scanning hidden autostart entries ... scanning hidden files ... scan completed successfully hidden files: 0 ************************************************** ************************ . Pre-Run: 8,112,275,456 bytes free Post-Run: 8,214,716,416 bytes free
|
|
#
6
27-04-2008, 07:29 PM
|
||||
|
||||
HJT log help
Looks good. How is everything now?
Time to do some cleanup and secure the work you have done.
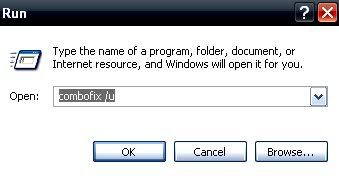
The above procedure will:
Setting a new restore point AFTER cleaning your system will enable your computer to roll-back to a clean working state if needed.
Out of date software has security vulnerabilities that malware can exploit.
Also see < Link hidden. Register for free to see this link! > for free cleaning/maintenance tools to help keep your computer running smooth.
__________________
.
Never argue with an idiot. They'll bring you down to their level, then beat you with experience.
.
.
|
|
|
|
| Thread Tools | |
 Show Printable Version  Email this Page |
|
|
Powered by vBulletin® Copyright ©2000 - 2008 Jelsoft Enterprises Ltd.
SEO by vBSEO ©2008, Crawlability, Inc.
|


